PHP flaw takes down websites worldwide
Patch lands two days after vulnerability in language powering 70 percent of the web goes public, NSA tells unpatched organizations to unplug while OpenAI claims credit for the discovery
Images
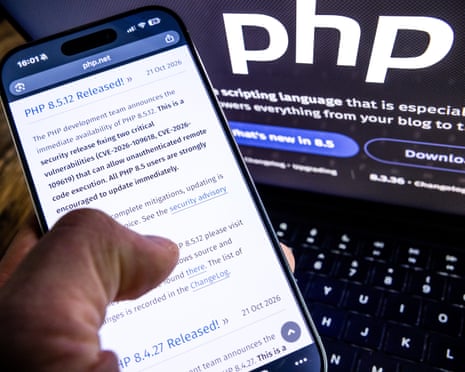 The PHP Foundation has released a patch for the flaw but it may take time for vulnerable sites to use it to shore up their defences. Photograph: ANP/Shutterstock
theguardian.com
A serious vulnerability in PHP — the programming language behind roughly 70 percent of the world's websites — forced emergency takedowns of public services across Europe on Wednesday, days after the flaw became public and security agencies in Washington and London issued warnings.
The PHP Foundation released a patch on Wednesday after researchers testing cyberdefences discovered the flaw. The US National Security Agency advised all organizations running PHP to take their systems offline if they could not patch immediately, noting the bug could "provide a direct path to the server's file system or database." The UK's National Cyber Security Centre told organizations to check for backdoors an attacker may already have installed.
The takedowns were immediate and broad. The Wikimedia Foundation pulled several systems offline as a precaution. Websites belonging to Edinburgh, Bristol and Oxford councils went dark, as did the Paris police prefecture's site. In the Netherlands, the national digital identity service, the house of representatives' website, and the national cybersecurity centre itself were all taken offline — the body charged with defending Dutch networks briefly unable to host its own. Sites in Germany, Belgium, Finland and France also reported disruption. WordPress, Wikipedia and Slack all run on PHP, and much of Facebook historically did.
OpenAI said it led the coalition of researchers who found the flaw and credited "frontier AI" with the discovery. The researcher who actually found the weakness said they did not use any models unavailable to the general public. One internet infrastructure expert warned that Russian state actors or large crime organizations could use vulnerable sites as launching pads for DDoS attacks, and that cryptocurrency miners could exploit unpatched servers at other people's expense.
The episode echoes the CrowdStrike outage in scale: a single defect in a foundational layer of software, patched under time pressure, with national agencies directing traffic. The difference is that this time the fix worked — and the agency telling everyone to unplug their servers was the same one whose warnings arrived only after the flaw was already public.